


A WebRTC STUN server is a lightweight protocol service that lets a client discover its public IP address and port as seen from the internet, which is essential for NAT traversal during ICE candidate gathering. STUN handles the majority of WebRTC connections on its own, while TURN servers act as a media relay fallback for the roughly 10 to 20 percent of networks where direct connectivity fails. This guide covers how STUN works, how to choose between hosted and self-hosted options, and how to deploy one for production using VideoSDK's WebRTC infrastructure.
Every WebRTC connection begins with a deceptively simple question: what is my public network address? Behind a home router, an office firewall, or a mobile carrier NAT, a device has no reliable way to answer that on its own. Without an answer, the ICE negotiation that powers real-time video and audio calls collapses before a single media packet flows. That discovery step is exactly what a WebRTC STUN server solves.
If you are building video calling, audio rooms, or interactive live streaming, STUN is one of the first infrastructure pieces you will encounter. Get it right and connections just work. Get it wrong and you spend weeks debugging one-way audio and failed calls. This guide walks through what a STUN server does, how it works at the protocol level, how to choose between public and self-hosted options, and how to run one reliably in production.
What Is a STUN Server?
STUN is defined as Session Traversal Utilities for NAT, a standardized protocol (RFC 5389 and its successor RFC 8489, published by the IETF) that lets a client discover its public IP address and port mapping as observed by a remote endpoint. A STUN server works by receiving a binding request from the client over UDP or TCP and echoing back the source address it observed, which reveals the NAT's external mapping for that connection.
Within WebRTC, STUN is a supporting actor in the larger ICE (Interactive Connectivity Establishment) framework. ICE gathers candidates from every available network path: local host addresses, server-reflexive addresses obtained via STUN, and relayed addresses obtained via TURN. It then tests pairs of candidates in priority order until it finds one that carries media successfully. STUN is the cheapest of these discovery mechanisms, which is why every WebRTC application configures at least one STUN server by default.
The difference between STUN and TURN is a common point of confusion. STUN only helps peers discover each other's public addresses; media still flows directly peer to peer. TURN, by contrast, is a relay: when direct connectivity fails, typically on symmetric NATs or restrictive corporate firewalls, TURN forwards every media packet through the server. STUN is cheap and stateless, while TURN is stateful, bandwidth-heavy, and expensive to run. A production WebRTC deployment needs both, with STUN doing the heavy lifting and TURN catching the edge cases.
If you would rather not manage this infrastructure yourself, VideoSDK's video calling SDK handles STUN, TURN, and full ICE orchestration behind its Rooms-based architecture, so you can focus on your application instead of NAT traversal.
How STUN Works Under the Hood
A STUN transaction is a single request and response exchange that completes in well under a second on a healthy network. Understanding the mechanics helps you debug candidate gathering when calls fail.
The process starts when the WebRTC stack, during ICE gathering, sends a binding request to the configured STUN server over UDP. The request contains a transaction identifier, a random 96-bit value that lets the client match the response to the request, plus optional attributes such as software version and fingerprint. The server does almost no work: it reads the source IP and port of the incoming packet and constructs a success response containing an XOR-MAPPED-ADDRESS attribute, which encodes the observed public address and port using an XOR operation against the transaction ID and a fixed magic cookie value.
When the client receives that response, it learns its server-reflexive candidate, the public address that remote peers should target. The client also distinguishes success responses from error responses, such as a 420 Unknown Attribute or a 400 Bad Request, which usually indicate a protocol version mismatch or a malformed request. Because the mapping a NAT creates can differ per destination, some NATs assign a new external port for every remote endpoint, STUN discovery is performed per candidate path, not once globally.
Here is the full request and response cycle in context:
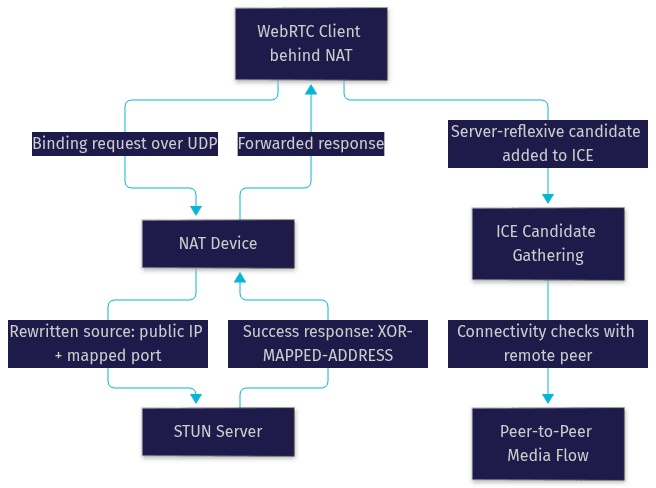
One detail worth internalizing: STUN tells the client what the server saw, not what every remote peer will see. On symmetric NATs, the mapping observed by the STUN server differs from the mapping observed by the actual remote peer, which is precisely why those connections fail and why TURN exists as the fallback. You can read more about how VideoSDK handles these edge cases automatically in its concept and architecture documentation.
Choosing Between Hosted and Self-Hosted STUN Servers
The first real decision is whether to use a public hosted STUN service or run your own. Both are valid; the right answer depends on your scale, latency requirements, and compliance posture.
Public STUN servers, such as Google's public STUN endpoints operated on the stun.l.google.com hostname, are free, globally distributed, and require zero maintenance. For prototypes, side projects, and early-stage products, they are perfectly adequate. The tradeoffs are real, though. You have no uptime guarantee, no visibility into latency or load, no control over rate limits, and no ability to promise a regulator that your signaling metadata never touches a third party. Public STUN services have also been subject to abuse for traffic amplification, so operators periodically throttle or restrict them.
A self-hosted STUN server gives you control over all of those variables. You can place instances close to your users to cut discovery latency, enforce rate limits and IP whitelisting, and keep every packet inside infrastructure you own. The cost is operational: you maintain the daemon, monitor it, keep it patched, and handle capacity as you grow. For most production teams, the pragmatic path is starting with public STUN for development, then standing up dedicated instances before launch.
| Factor | Hosted / Public STUN | Self-Hosted STUN |
|---|---|---|
| Cost | Free | Server plus ops time |
| Latency control | None, depends on provider | Full, place near users |
| Uptime guarantee | Best effort | Your own SLA |
| Security controls | None | Rate limiting, whitelisting, TLS |
| Compliance fit | Weak for regulated data | Strong |
| Maintenance burden | Zero | Ongoing |
| Best for | Prototypes, small apps | Production, regulated industries |
The most important row is latency control. STUN discovery happens at the start of every call, so a slow STUN server directly delays time-to-first-frame. If your users are regionally concentrated, a self-hosted instance in the same region will consistently beat a public service that may resolve from another continent.
Setting Up a Self-Hosted WebRTC STUN Server
Running your own STUN server is one of the lighter infrastructure tasks in real-time communication, but the details matter. This section walks through the full setup in plain terms.
Prerequisites
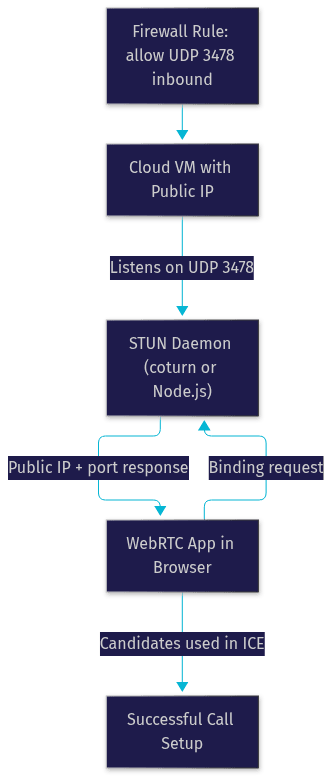
Before installing anything, confirm four things. First, you need a server with a publicly reachable IP address, a small cloud VM is fine since STUN is stateless and lightweight. Second, your firewall must allow inbound UDP traffic on your chosen listening port, which is 3478 by convention. Third, decide whether you need TLS-protected STUN: standard STUN runs over plain UDP, while TLS-STUN runs over TLS over TCP for environments that block or inspect UDP. Fourth, if you plan to also run TURN on the same box later, as most teams eventually do with coturn, provision for that now in terms of bandwidth and open ports.
Installation Approaches
There are two popular routes. The first is a Node.js-based STUN package such as @msimerson/stun, which you install as a dependency and run as a small Node process. It is a good fit when your stack is already JavaScript-based and you want STUN colocated with your signaling server. The second and more common route is coturn, a mature C-based daemon that bundles STUN and TURN together. Most production deployments standardize on coturn because you get the TURN relay fallback in the same process, configured through a single settings file.
With either approach, the setup intent is the same: start a process that listens on UDP port 3478 on the server's public interface, verify it responds to binding requests from an external network, and then reference the server in your WebRTC configuration by its public address and port. With coturn, the key configuration knobs include the listening port, the external IP address the server should advertise (critical when running behind cloud NATs where the machine's local interface differs from its public IP), the realm and long-term credentials if you enable authentication for TURN, and TLS certificate paths if you terminate TLS-STUN.
Verifying the Deployment
After starting the server, test it from a device on a different network, not from the server itself, since a local test cannot exercise NAT traversal. A successful check returns your device's public IP and mapped port within a few hundred milliseconds. Then point a real WebRTC application at the server and confirm that server-reflexive candidates appear during ICE gathering. If they do, discovery is working.
If you would rather skip this entire layer, the VideoSDK Prebuilt UI Kit embeds a working video calling interface with all connectivity infrastructure handled for you.
Best Practices for Production STUN Deployments
A STUN server that works in development is not the same as one that survives production traffic. These practices separate the two.
Redundancy first. Because STUN is stateless, redundancy is cheap: run at least two instances in different geographic regions and list both in your WebRTC configuration. The ICE stack tries candidates from each, so a single dead server adds a small delay rather than breaking calls. Teams with global users commonly run three or more instances and route users to the nearest one.
Monitor discovery latency and success rate. The two metrics that matter are the round-trip time of binding requests and the ratio of successful responses to errors. A healthy STUN server responds in under 100 milliseconds from the same region; sustained latency spikes mean users experience slower call setup. Health checks should probe the server externally on a schedule and page you when the success rate drops.
Lock down security. Even though STUN leaks no media content, an open server can be abused. Apply rate limiting per source IP to blunt amplification and scraping attacks, whitelist your application's infrastructure where feasible, and enable TLS-STUN for TCP-based clients in restrictive network environments. Keep the daemon updated, since STUN implementations have had CVEs historically.
Plan the TURN fallback. STUN alone connects roughly 80 to 90 percent of network configurations; symmetric NATs, carrier-grade NATs, and strict corporate firewalls need a relay. Design your deployment so a TURN server sits alongside STUN from day one, and monitor what fraction of your calls fall back to relay, since that number drives your bandwidth costs. VideoSDK deployments handle this automatically with network-adaptive infrastructure, and you can inspect session-level behavior through the VideoSDK REST API.
Common Pitfalls and Troubleshooting
Most STUN failures trace back to a handful of root causes. Work through this checklist in order when calls fail to connect.
Symmetric NAT requiring TURN. If ICE gathering succeeds but connectivity checks fail, and candidates show different mapped ports per destination, the network is symmetric. No STUN configuration fixes this. The solution is a TURN relay, not more STUN servers.
Misconfigured public IP. On cloud VMs behind provider NAT, the daemon often binds to the machine's private interface and advertises the wrong address. The symptom is server-reflexive candidates that are unreachable. The fix is explicitly configuring the external public IP in the daemon settings so responses carry the correct address.
Firewall blocking UDP 3478. The classic silent failure: the server runs, local tests pass, and remote clients get nothing. Verify the cloud security group and host firewall both allow inbound UDP on the listening port, and remember that some corporate networks block UDP entirely, which is when TLS-STUN over TCP or a TURN fallback saves the call.
Stale or dead public STUN entries. Applications hardcoding public STUN addresses from old tutorials frequently break when those services change. Reference current, maintained endpoints and test them periodically.
A practical debugging flow: confirm the server responds externally, confirm server-reflexive candidates appear in ICE gathering, confirm connectivity checks pass between peers, and only then suspect media-level issues. Following that order isolates the failing layer quickly, and the WebRTC statistics API exposes ICE candidate types and state transitions that make each step verifiable.
Quick Answers to Top Developer Queries
A few questions come up constantly. The standard STUN port is UDP 3478. Yes, you can run multiple STUN servers in one configuration, and you should, for redundancy. No, STUN cannot relay media; that is TURN's job. Public STUN servers are free but carry no guarantees, so production systems should own their infrastructure. And latency matters: because discovery precedes every call, a slow STUN server measurably delays call setup time.
For teams evaluating whether to build this layer themselves or consume it as a service, the honest comparison is this: raw WebRTC with self-managed STUN and TURN gives maximum control at maximum operational cost, while a managed SDK like VideoSDK gives you sub-300ms latency, multi-platform SDKs, and built-in recording and transcription without maintaining any traversal infrastructure. The VideoSDK code samples show both paths in practice.
Definitions Glossary
STUN Server: A protocol service implementing Session Traversal Utilities for NAT that tells a WebRTC client its public IP address and port as observed from the internet, enabling NAT traversal during ICE candidate gathering.
ICE (Interactive Connectivity Establishment): The WebRTC framework that gathers host, server-reflexive, and relayed candidates, then tests candidate pairs in priority order until a working media path is found.
TURN Server: A stateful relay that forwards all media packets between peers when direct connectivity fails, typically on symmetric NATs or restrictive firewalls; expensive but necessary for roughly 10 to 20 percent of networks.
Server-Reflexive Candidate: The public address and port a client learns from a STUN binding response, added to the ICE candidate list for connectivity checks with remote peers.
XOR-MAPPED-ADDRESS: The STUN response attribute that encodes the client's observed public address using an XOR operation against the transaction ID and magic cookie, per RFC 8489.
Symmetric NAT: A NAT type that assigns a different external port mapping for every destination, making STUN-discovered addresses unusable for other peers and forcing a TURN fallback.
Key Takeaways
- A WebRTC STUN server is a stateless, lightweight service that discovers public addresses during ICE gathering, and it is the cheapest and first connectivity mechanism every WebRTC app uses.
- STUN succeeds for most networks, but symmetric NATs and strict firewalls require a TURN relay fallback, so production deployments need both.
- Public STUN services like Google's are fine for prototypes, but production systems benefit from self-hosted instances for latency control, security, and compliance.
- The most common failures are a misconfigured public IP on cloud VMs, firewalls blocking UDP 3478, and symmetric NATs misdiagnosed as STUN problems.
- Managed platforms like VideoSDK eliminate this entire infrastructure layer, bundling STUN, TURN, and adaptive networking into SDKs across ten-plus platforms.
Conclusion
A well-chosen WebRTC STUN server is the difference between calls that connect instantly and support tickets about one-way audio. Start with public STUN for development, stand up redundant self-hosted instances before launch, pair them with a TURN fallback, and monitor discovery latency like any other critical dependency. Or skip the plumbing entirely: VideoSDK handles NAT traversal, media routing, and adaptive streaming for you, with a free tier to get started at app.videosdk.live/login. What are you building with WebRTC? Drop a comment, I'd love to hear what kind of real-time communication use case you're working on.
Advanced Applications of Stun Server
Security Considerations for Stun Server
While STUN servers are essential for NAT traversal and peer-to-peer communication, they must be configured and managed with security in mind to prevent vulnerabilities and attacks.
1. Common Vulnerabilities
- IP Address Spoofing: Attackers can spoof IP addresses to bypass security measures or disrupt communication.
- Denial of Service (DoS) Attacks: High volumes of STUN requests can overwhelm the server, leading to service outages.
- Information Exposure: Sensitive information, such as IP addresses and network topology, can be exposed if STUN responses are intercepted.
2. Best Practices for Secure Deployment
- Enable Authentication: Implement long-term credential mechanisms to ensure that only authorized clients can access the STUN server.
- Use Encryption: Protect STUN messages with Transport Layer Security (TLS) to prevent interception and tampering.
- Rate Limiting: Configure rate limiting to mitigate the risk of DoS attacks by controlling the number of requests from each client.
3. Example Code Snippets for Enhancing Security
Enabling Authentication:
bash
1lt-cred-mech
2user=username:password
Using Encryption:
bash
1tls-listening-port=5349
2cert=/etc/ssl/certs/turn_server_cert.pem
3pkey=/etc/ssl/private/turn_server_pkey.pem
Configuring Rate Limiting:
bash
1no-cli
2cli-ip=127.0.0.1
3cli-port=5766
4cli-password=your_password
5stale-nonce
By following these best practices and implementing robust security measures, you can protect your STUN server from common threats and ensure reliable and secure communication.
Conclusion
STUN servers are indispensable components in real-time communication systems like WebRTC and VoIP, enabling devices behind NATs to establish direct connections efficiently. By understanding their operation, configuration, and integration, developers can build robust applications that traverse network obstacles seamlessly. Moreover, with advanced configurations and security considerations, STUN servers can offer enhanced performance and protection against vulnerabilities. Embracing these principles ensures the reliability, security, and scalability of real-time communication.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ