

The RBI video KYC guidelines are the V-CIP (Video-based Customer Identification Process) rules in the Reserve Bank's KYC Directions, 2025. On 28 November 2025 the RBI replaced the 2016 KYC Master Direction with ten Directions, one for each type of regulated entity. For a commercial bank, V-CIP is paragraphs 26 and 27 of the Commercial Banks KYC Directions, 2025 (RBI/DOR/2025-26/169). Every one of the ten says the entity "may undertake V-CIP", so it is optional. Once an entity offers it, every session must meet the minimum standards: a specially trained official runs a live, consented, recorded call, the system can block connections from IP addresses outside India, the recording carries live GPS and a time stamp, and all data is stored in India.
This guide is for compliance, product and engineering teams at banks, NBFCs and other RBI-regulated entities, and for the fintechs that build video KYC for them. It shows which Direction and paragraph applies to you, what each rule asks of the video layer, what evidence an auditor will want, and which common claims about V-CIP are not in the RBI text.
How VideoSDK checked this guide: we compared the ten V-CIP texts word by word, and paragraph 18 of the 2016 Master Direction with paragraphs 26 and 27 of the Commercial Banks Directions, sentence by sentence. The three code samples were run against @videosdk.live/react-sdk 1.2.0 and the live VideoSDK API, and what we could not run is stated under each sample. The middle and right columns of the clause tables are our reading for engineering and audit teams, not legal advice.
Key takeaways
- The 2016 KYC Master Direction is repealed. V-CIP now lives in ten entity-wise KYC Directions, all dated 28 November 2025. Commercial banks: paras 26 and 27 of RBI/DOR/2025-26/169. NBFCs: paras 26 and 27 of RBI/DOR/2025-26/361.
- V-CIP is optional ("may undertake V-CIP"). If an entity offers it, it must be the first option for remote onboarding (para 44(1) for commercial banks).
- The minimum standards are the same in all ten texts. One substantive difference: assisted V-CIP through Business Correspondents appears only in the seven bank Directions, not in the NBFC, AIFI or ARC ones.
- The video layer carries most of the rules: block IP addresses outside India, geo-tag the recording with live GPS and a timestamp, keep one video file per session, start a fresh session after a call drop, and store all data and recordings in India.
- Apart from renumbering and firmer wording ("should" became "shall"), the only new V-CIP text in the 2025 Directions is an Explanation in the liveness clause: blinking, smiling or other gestures are not mandatory, and the customer's special needs must be considered.
- There is no V-CIP-specific retention period. The general record rule keeps identification records for at least five years after the business relationship ends (para 50(2)).
What is V-CIP and how does the process work?
The Commercial Banks Directions define V-CIP as "an alternative method by which an authorised official of the bank conducts customer identification with facial recognition and customer due diligence" (para 5(2)(xvi)). The session is a live, consent-based audio and video interaction, and a bank must treat a V-CIP that meets the prescribed standards "on par with face-to-face CIP".
Two things follow from that definition:
- A trained official of the regulated entity runs the call. Para 27(2)(i) says the process "shall be operated only by officials of the bank specially trained for this purpose". A flow in which the customer only follows automated prompts, with no official on the call, is not V-CIP. AI can support the official (para 27(1)(vi) says the bank "may use appropriate artificial intelligence (AI) technology"), but it cannot replace them.
- It is identification and due diligence, not a selfie check. The official collects identity data from one of four sources, sees the PAN card, matches faces across documents, confirms the customer's address and financial profile, and records the whole interaction.
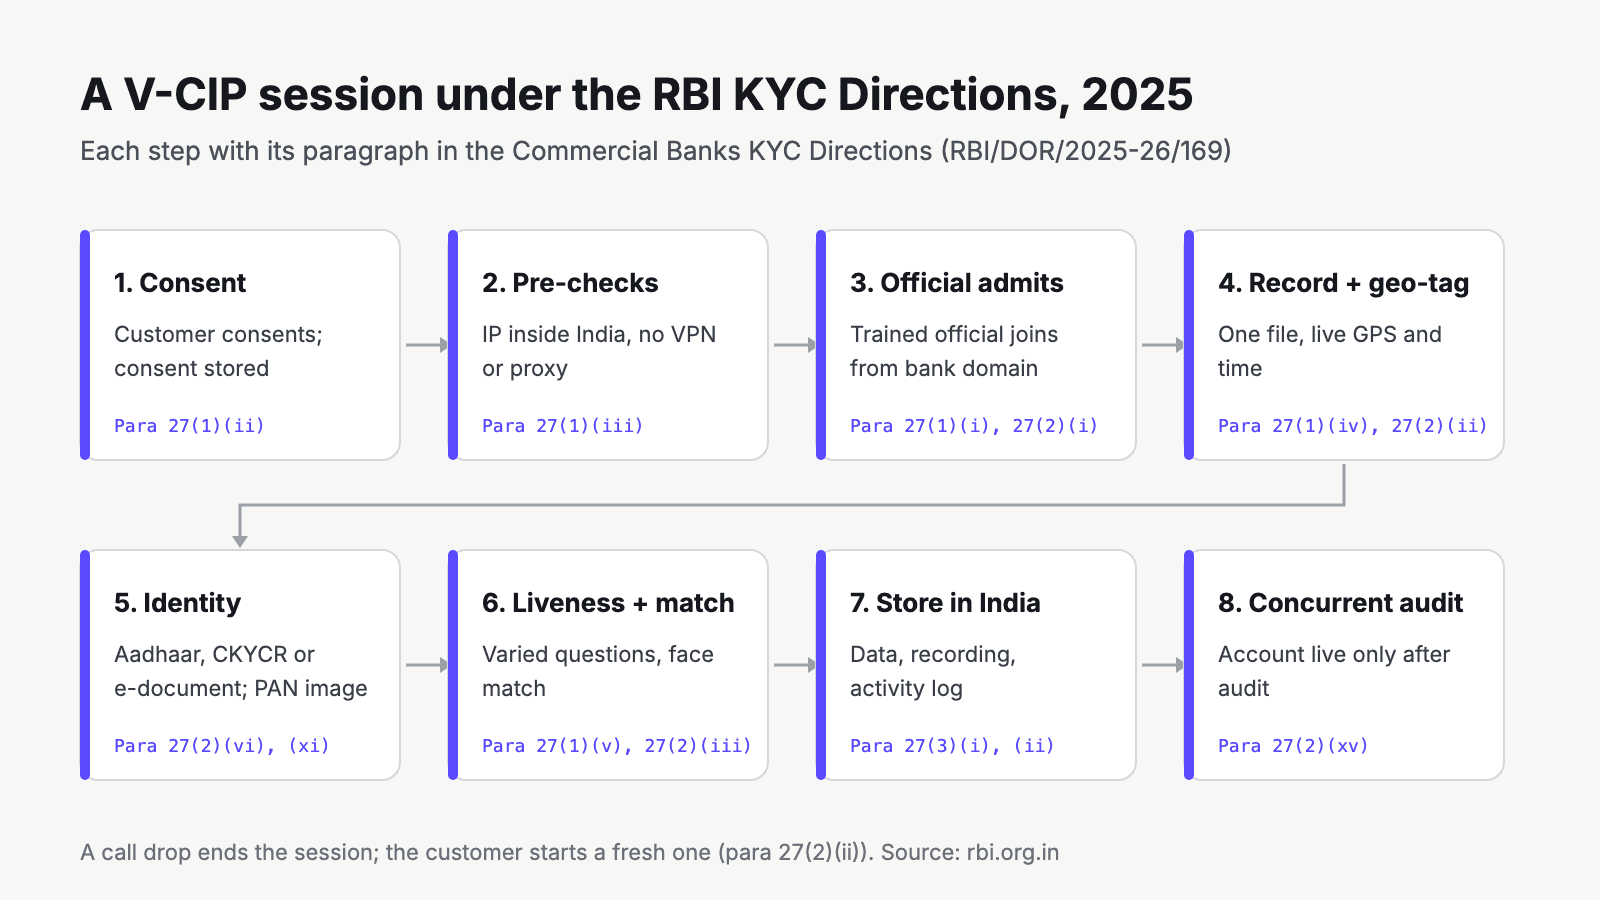
In practice a session runs in this order: the customer consents, the system checks that the connection comes from India, a trained official admits the customer, recording starts with live GPS and time, the official verifies identity, PAN and liveness, the data is stored in India, and a concurrent auditor checks the account before it goes live. The diagram in the rules section below maps each step to its paragraph.
Our explainer on what V-CIP is and how video KYC works covers the basics from the customer's side. This page covers the rules.
Which RBI KYC Direction applies to you
Each type of regulated entity now has its own KYC Directions, 2025. The V-CIP text is the same in all of them; the paragraph numbers differ. All ten were issued on 28 November 2025 and are listed on the RBI's Master Directions page.
| Regulated entity | KYC Directions, 2025 | V-CIP uses | V-CIP minimum standards | V-CIP as first option | 5-year record rule |
|---|---|---|---|---|---|
| Commercial banks | RBI/DOR/2025-26/169 | 26 | 27 | 44(1) | 50(2) |
| Small finance banks | RBI/DOR/2025-26/200 | 27 | 28 | 45(1) | 51(2) |
| Payments banks | RBI/DOR/2025-26/218 | 26 | 27 | 44(1) | 49(2) |
| Local area banks | RBI/DOR/2025-26/243 | 25 | 26 | 43(1) | 49(2) |
| Regional rural banks | RBI/DOR/2025-26/266 | 25 | 26 | 43(1) | 49(2) |
| Urban co-operative banks | RBI/DOR/2025-26/291 | 25 | 26 | 43(1) | 49(2) |
| Rural co-operative banks (state and central) | RBI/DOR/2025-26/316 | 25 | 26 | 43(1) | 49(2) |
| All India financial institutions | RBI/DOR/2025-26/335 | 26 | 27 | 43(1) | 47(2) |
| NBFCs | RBI/DOR/2025-26/361 | 26 | 27 | 44(1) | 47(2) |
| Asset reconstruction companies | RBI/DOR/2025-26/377 | 25 | 26 | 43(1) | 45(2) |
VideoSDK compared the ten V-CIP texts word by word. The substance matches, with three differences:
- Assisted V-CIP. The bank texts say the bank "shall permit assisted V-CIP when it takes help of Business Correspondents (BCs) to facilitate the process only at the customer end" (27(2)(xiv) for commercial banks). The NBFC, AIFI and ARC texts have no such clause, so their concurrent audit clause is numbered (xiv) instead of (xv).
- Cyber security framework. Each text points to the RBI cyber security framework for its own entity type.
- Numbering of uses. The NBFC text numbers the proprietorship-firm proviso as a separate item, so its uses run from (1) to (4).
Paragraph numbers in the rest of this guide follow the Commercial Banks Directions. If you are an urban co-operative bank, take one off (27 becomes 26); for a small finance bank, add one (27 becomes 28). Do not apply a fixed shift for other entity types: for NBFCs, for example, V-CIP stays at 26 and 27 and the first-option rule at 44(1), but the record rule moves from 50(2) to 47(2), so read your row in the table above. Our guide to video KYC for co-operative and small finance banks covers those Directions in detail.
NBFCs, housing finance companies, NBFC-MFIs and P2P lending platforms all follow the NBFC KYC Directions. Our guide to video KYC for NBFCs walks through paras 26 and 27 of that text clause by clause, with tested build code.
Is V-CIP optional for banks and NBFCs?
Yes. Every Direction says the entity "may undertake V-CIP". What is compulsory is the order of options: if a bank has introduced V-CIP, "it shall provide the same as the first option to the customer for remote onboarding" (para 44(1)), and it must treat a compliant V-CIP as equal to face-to-face identification. The Directions also keep other routes, such as face-to-face identification at a branch.
What V-CIP can be used for
Para 26 lists three uses:
- Customer due diligence (CDD) for new customers: individuals, the proprietor of a proprietorship firm, and the authorised signatories and beneficial owners of legal entities. For a proprietorship firm, the bank must also obtain the equivalent e-documents of the firm's activity proofs.
- Converting accounts opened with Aadhaar OTP e-KYC. Accounts opened in non-face-to-face mode with Aadhaar OTP carry limits (for example, the aggregate deposit balance "shall not exceed Rupees One Lakh", para 25(3)) and cannot run beyond one year unless the customer completes full identification, for which V-CIP is one route (para 25(6)).
- Updation and periodic updation of KYC for eligible customers, which makes V-CIP a channel for re-KYC campaigns.
V-CIP covers identity and KYC updation, not credit appraisal. The credit officer's video interview before a loan is sanctioned is a separate step under the lender's credit policy; see our guide to Video PD for loan underwriting.
RBI video KYC guidelines, clause by clause
These are the RBI video KYC guidelines in full: the minimum requirements in para 27 of the Commercial Banks Directions, with what each one asks of the video layer and what an auditor is likely to ask you to show. The quotes are from the RBI text; the middle and right columns are our reading for engineering and audit teams, not legal advice.
Infrastructure (para 27(1))
| Rule | Para | What it means for the video layer | Evidence to keep |
|---|---|---|---|
| Comply with the RBI cyber security framework; house the technology "in its own premises"; the connection must "originate from its own secured network domain" | 27(1)(i) | The V-CIP application runs inside the bank's network domain; vendor components are outsourcing and follow RBI outsourcing rules | Architecture diagram, outsourcing assessment |
| If cloud is used, data ownership "rests with the bank only", all data including video moves to the bank's own or leased servers "immediately after the V-CIP process is completed", and the provider "shall retain no data" | 27(1)(i) | Recordings and images go straight to a bucket the bank owns; the video provider keeps no copy | Storage configuration, provider's data deletion terms |
| "End-to-end encryption of data between customer device and the hosting point of the V-CIP application" | 27(1)(ii) | Encrypt every hop from the customer's device to the bank's hosting point (see the encryption note below) | Encryption design, security test report |
| Record customer consent "in an auditable and alteration-proof manner" | 27(1)(ii) | A consent step before the call starts, stored with a timestamp | Consent log |
| Prevent "connection from IP addresses outside India or from spoofed IP addresses" | 27(1)(iii) | IP geolocation check and VPN or proxy detection before the join | Configuration, test cases with a foreign IP and a VPN |
| Recordings "shall contain the live GPS co-ordinates (geo-tagging) of the customer" and a date and time stamp; video quality "adequate to allow identification of the customer beyond doubt" | 27(1)(iv) | Capture device GPS during the call and write it, with time, into the recording itself | Sample recordings showing coordinates and time |
| Face liveness or spoof detection and face matching "with high degree of accuracy" | 27(1)(v) | A liveness and face match component; gestures such as blinking are not mandatory | Vendor accuracy reports, test results |
| AI may be used | 27(1)(vi) | Optional AI checks to support the official | Model documentation if used |
| Update technology from detected, attempted and near-miss fraud; report forged identity "as a cyber event" | 27(1)(vii) | Feedback loop from fraud cases into the app and workflows | Incident register, change log |
| VAPT and security audit before roll-out, by "empanelled auditors of Indian Computer Emergency Response Team (CERT-In)", repeated periodically | 27(1)(viii) | Fix every critical finding before go-live | CERT-In empanelled auditor reports, closure evidence |
| Functional, performance and maintenance testing of the application and its APIs before live use | 27(1)(ix) | Load and failure testing of the video and API stack | Test reports |
Procedure (para 27(2))
| Rule | Para | What it means for the video layer | Evidence to keep |
|---|---|---|---|
| A written workflow and SOP; only specially trained officials; liveness check "shall not result in exclusion of person with special needs" | 27(2)(i) | Official's console follows the SOP; an accessible path for customers who cannot do a gesture | SOP, training records |
| Pauses or reconnects "may not result in creation of multiple video files"; "in case of call drop / disconnection, fresh session shall be initiated" | 27(2)(ii) | One recording file per session; a dropped call ends the session and the customer starts again | Recording logs, session logs |
| Vary the sequence or type of questions to show the call is live | 27(2)(iii) | Randomised question sets on the official's console | Question bank, session notes |
| Reject the application on "any prompting at the customer end" | 27(2)(iv) | Official can end and reject; audio of the room is in the recording | Rejection log |
| Check existing customer, earlier rejection and negative lists | 27(2)(v) | Screening step in the workflow | Screening results |
| Record audio and video, capture a photograph, and take identity data from Aadhaar OTP e-KYC, offline Aadhaar, CKYCR or an equivalent e-document (including DigiLocker) | 27(2)(vi) | Recording plus a still capture of the customer's face | Recording, photo, identity source used |
| Redact or black out the Aadhaar number | 27(2)(vii) | Mask the number in captures and stored documents | Masked samples |
| Offline Aadhaar XML or QR "not older than three working days"; video step within three working days of obtaining the data | 27(2)(viii), (ix) | Check document dates before the call | Timestamps of download and call |
| Capture current address records if different; confirm economic and financial profile | 27(2)(x) | Questions and captures in the script | Session notes |
| Capture a clear image of the PAN card unless e-PAN is given; verify PAN with the issuing authority | 27(2)(xi) | High-resolution capture from the customer's camera | PAN image, verification response |
| A printed copy of an e-document, including e-PAN, is not valid | 27(2)(xii) | Official rejects printouts held up to the camera | SOP, rejection log |
| Photo in Aadhaar or OVD and PAN must match the customer; details must match | 27(2)(xiii) | Face match across the live face and the document photos | Match results |
| Assisted V-CIP through BCs at the customer end; keep the BC's details | 27(2)(xiv) | Support a BC device or tablet at the customer's side | BC details per session |
| Accounts operational "only after subjecting them to concurrent audit" | 27(2)(xv) | Hand-off from the session to a concurrent auditor before activation | Audit sign-off |
| Comply with other statutes such as the IT Act | 27(2)(xvi) | Data protection and IT Act obligations apply | Legal review |
Records and data (para 27(3))
| Rule | Para | What it means for the video layer | Evidence to keep |
|---|---|---|---|
| Store "the entire data and recordings of V-CIP in a system / systems located in India", safe, secure and with date and time stamps that allow easy search | 27(3)(i) | Recordings and captures in an India region bucket the bank controls | Storage region settings, search index |
| Record management rules of the Directions apply to V-CIP | 27(3)(i) | Retention follows para 50 | Retention policy |
| Preserve "the activity log along with the credentials of the official performing the V-CIP" | 27(3)(ii) | Join and leave times, actions and the official's ID per session | Activity log export |
Did the RBI V-CIP rules change in 2025?
Mostly no: the 2025 Directions carry over every V-CIP requirement. VideoSDK compared paragraph 18 of the repealed 2016 Master Direction (as last amended on 14 August 2025) with paragraphs 26 and 27 of the Commercial Banks Directions, sentence by sentence. Every 2016 requirement carries over. Most changes are wording ("should" became "shall") and renumbering. The one new piece of V-CIP text is the Explanation under the liveness clause:
"Making specific facial gestures, like blinking of eyes, smiling, frowning, etc. is not mandatory for liveness check. The bank shall take due cognizance of special needs, if any, of the customer during liveness check." (para 27(1)(v))
If your vendor documents, SOPs or audit checklists still cite 2016 paragraph numbers, use this map:
| Topic | 2016 Master Direction | Commercial Banks Directions, 2025 |
|---|---|---|
| Definition of V-CIP | para 3 | 5(2)(xvi) |
| Aadhaar OTP e-KYC accounts and their limits | 17 | 25 |
| V-CIP uses | 18 | 26 |
| V-CIP minimum standards | 18(a) to (c) | 27(1) to (3) |
| V-CIP as first option for remote onboarding | 40(a) | 44(1) |
| Record keeping (five years) | 46 | 50(2) |
| Repeal of the earlier instructions | - | 80 |
V-CIP timeline
- 9 January 2020: the RBI adds V-CIP to the 2016 KYC Master Direction (RBI/2019-20/138).
- 10 May 2021: V-CIP rewritten with three uses (new customers, conversion of Aadhaar OTP accounts, periodic updation) and detailed minimum standards, including the block on IP addresses outside India (RBI/2021-22/35).
- 28 April 2023: amendments add V-CIP for proprietorship firms, the cloud deployment rule, the single-video-file rule for disruptions, and the three-working-day limit for Aadhaar XML or QR (RBI/2023-24/24).
- 17 October 2023: three-working-day window for completing the video step after obtaining identity data (RBI/2023-24/69).
- 14 August 2025: "The liveness check shall not result in exclusion of person with special needs" (RBI/2025-26/75).
- 28 November 2025: ten entity-wise KYC Directions issued; the 2016 Master Direction repealed (para 80 of the Commercial Banks Directions).
The amendments made to the Commercial Banks Directions since then (29 December 2025 on CKYCR, 18 September 2026 on foreign portfolio investors, 1 October 2026 on governance) do not touch paras 26 and 27.
What are the common myths about the RBI video KYC rules?
These are common claims about V-CIP, some of them on pages that rank for these searches (for example, unassisted AI-only flows and "5 years from session" retention). Each was checked against the Commercial Banks Directions.
| Claim | What the Directions say |
|---|---|
| "V-CIP is mandatory for banks" | Optional: "may undertake V-CIP". If offered, it must be the first option for remote onboarding (44(1)). |
| "V-CIP recordings must be kept for 5 years from the session" | No V-CIP-specific period. The record rule keeps identification records "for at least five years after the business relationship has ended" (50(2)), and 27(3)(i) applies the record rules to V-CIP. |
| "The customer must blink or smile for liveness" | Gestures are "not mandatory for liveness check" (27(1)(v) Explanation). |
| "AI can run video KYC without an official" | Only "officials of the bank specially trained for this purpose" may operate V-CIP (27(2)(i)). AI may support them (27(1)(vi)). |
| "The official must sit in a branch" | No rule on the official's location. The rule is that the connection originates from the bank's "own secured network domain" (27(1)(i)). |
| "There is a minimum bandwidth" | No figure. The rule is that video quality must allow identification "beyond doubt" (27(1)(iv)). |
| "A 2026 RBI circular changed V-CIP" | We found no 2026 RBI instruction that amends the V-CIP paragraphs. |
| "Reconnecting after a drop keeps the same session" | A call drop needs a fresh session; only pauses that do not create multiple files may continue (27(2)(ii)). |
What evidence does an auditor ask for in a V-CIP audit?
Before go-live and at each periodic review, have these ready:
- V-CIP workflow and SOP, with the training record of every official (27(2)(i))
- Architecture diagram showing own premises or cloud, the network domain and every vendor component (27(1)(i))
- CERT-In empanelled auditor's VAPT and security audit report, with closure of every critical gap (27(1)(viii))
- Functional, performance and API test reports (27(1)(ix))
- Test cases for a foreign IP address and a VPN connection (27(1)(iii))
- Sample recordings showing GPS coordinates and time, one file per session (27(1)(iv), 27(2)(ii))
- Liveness and face match accuracy evidence, and the path for customers with special needs (27(1)(v))
- Storage configuration showing India location for recordings, images and logs (27(3)(i))
- Activity log with the official's credentials for each session (27(3)(ii))
- Concurrent audit sign-off before each account is made operational (27(2)(xv))
- Retention policy that follows para 50
To work through every clause as a build task, a test and an evidence item, with a free CSV and PDF copy, use our video KYC compliance checklist.
Encryption and recording: read 27(1)(ii) carefully
The RBI asks for end-to-end encryption "between customer device and the hosting point of the V-CIP application". The hosting point is the bank's application, which also has to record the session. That is a different design goal from media end-to-end encryption between call participants, where no server can see the media.
This matters when you pick a platform. VideoSDK's E2EE page says recording and transcription are not supported while end-to-end encryption (E2EE) is on, and V-CIP requires a recording (27(2)(vi)). Agree the encryption design with your security team and your CERT-In empanelled auditor before you build, and talk to us about how a recorded session is protected in transit. Our guide to end-to-end encryption in video calls explains what E2EE does and does not cover.
For recordings at rest, VideoSDK's recording encryption encrypts each recording with AES-256-GCM or AES-256-CTR, with the key wrapped by your RSA public key. It cannot be turned on together with transcription and summaries on the same API key.
Turning the rules into a build with VideoSDK
VideoSDK provides the video layer: the call, recording, signalling and session data (see the video KYC solution overview). Your application provides the workflow, the official's console, identity checks and the audit trail. If you are still deciding whether to build that stack or buy a finished platform, our build vs buy guide covers the trade-offs. This is how the rules map to documented VideoSDK features. Items marked Enterprise need the Enterprise plan; contact sales to enable them.
| Rule | VideoSDK feature | Docs |
|---|---|---|
| Block IPs outside India (27(1)(iii)) | Geo IP Restriction by region, including INDIA; the docs list VPN and proxy restriction as a use case (Enterprise) | Geo IP Restriction |
| Data and recordings in India (27(3)(i)) | Geo Fencing keeps connections on servers in the chosen region, including INDIA (Enterprise); recordings go to your own AWS S3, Azure Blob or GCP bucket. Ask where session metadata, logs and messages are stored | Geo Fencing, storage configuration |
| Provider retains no data (27(1)(i)) | Recordings written to the bank's bucket; agree retention of call metadata in your contract | Storage configuration, above |
| GPS and time in the recording (27(1)(iv)) | Geo-tag recording template driven by PubSub (we did not test the template) | Geo tag recordings |
| Recording must not silently stop (27(2)(vi)) | onFailure: { action: "close-room" } on the start recording API | Start recording API |
| Official admits the customer | Waiting lobby with ask_join tokens and onEntryRequested | Video KYC guide |
| Photo and PAN capture (27(2)(vi), (xi)) | captureImage() on the customer's own camera, requested over PubSub | Video KYC guide, above |
| Fresh session after a call drop (27(2)(ii)) | Your app: when the customer leaves, end the room and create a new room for the retry | Create room API |
| Activity log (27(3)(ii)) | Sessions API with join and leave times; webhooks for session, participant and recording events | Fetch sessions, create room webhooks |
| Face match, spoof detection, OCR (27(1)(v), 27(2)(xiii)) | Identity verification APIs (Enterprise) | Face match, spoof detection |
The three samples below cover rules that the top-ranking pages we read explain but do not show in code: GPS in the recording, no session without a recording, and the activity log. We ran each one against @videosdk.live/react-sdk 1.2.0 and the live VideoSDK API in headless Chrome with an emulated camera and GPS position. What we could not run is noted under each sample.
Send the customer's GPS position to the official and the recording
The docs' geo-tag recording template reads coordinates from the PubSub topic GEO_TAG. This component sends the customer's position from the phone browser once the customer has joined.
// ShareLocation.jsx (customer page, inside <MeetingProvider>)
import { useCallback, useEffect, useRef, useState } from "react";
import { useMeeting, usePubSub } from "@videosdk.live/react-sdk";

export default function ShareLocation({ customerName }) {
  const [joined, setJoined] = useState(false);
  const [status, setStatus] = useState("Connecting...");
  const lastFix = useRef(null);
  const { publish } = usePubSub("GEO_TAG");

  const sendFix = useCallback(async () => {
    if (!lastFix.current) return;
    try {
      // persist: false: the coordinates are not stored with the session
      // (see 27(1)(i)); the re-send below covers late joiners.
      await publish("GEO TAG DATA", { persist: false }, lastFix.current);
      setStatus("Location shared with the bank official.");
    } catch (err) {
      setStatus("Could not send your location. Please stay on the call.");
    }
  }, [publish]);

  useMeeting({
    onMeetingJoined: () => setJoined(true),
    // Send the last fix again when the official or the recorder joins,
    // so nobody waits for the customer's next position change.
    onParticipantJoined: () => sendFix(),
  });

  useEffect(() => {
    if (!joined) return; // publish() throws error 3035 before the join.
    if (!navigator.geolocation) {
      setStatus("This browser cannot share location. Please switch browsers.");
      return;
    }
    const watchId = navigator.geolocation.watchPosition(
      ({ coords }) => {
        lastFix.current = {
          latitude: coords.latitude.toFixed(6),
          longitude: coords.longitude.toFixed(6),
          accuracy: Math.round(coords.accuracy),
          participantName: customerName,
        };
        sendFix();
      },
      () => setStatus("Please allow location access. The bank cannot continue without it."),
      { enableHighAccuracy: true, maximumAge: 0, timeout: 15000 }
    );
    return () => navigator.geolocation.clearWatch(watchId);
  }, [joined, sendFix, customerName]);

  return <p>{status}</p>;
}
On the official's console, show the latest fix and hold the identity checks until one arrives:
// LocationCheck.jsx (official's console, inside <MeetingProvider>)
import { usePubSub } from "@videosdk.live/react-sdk";

export default function LocationCheck() {
  const { messages } = usePubSub("GEO_TAG");
  const latest = messages.at(-1);

  if (!latest) return <p>No GPS location yet. Do not start the identity checks.</p>;

  const { latitude, longitude, accuracy } = latest.payload;
  return (
    <p>
      Customer GPS: {latitude}, {longitude} (within {accuracy} m), received at{" "}
      {new Date(latest.timestamp).toLocaleTimeString("en-IN")}
    </p>
  );
}
What our test run showed:
- Calling
publish()before the join fails with error 3035 ("You must join the meeting before calling the Publish() method."), which is why the location watch starts inonMeetingJoined. - In our runs, a participant who joined after the customer did not receive the earlier message, even with
persist: true. Sending the last fix again inonParticipantJoinedfixed it, so the sample usespersist: false. The docs saypersist: truekeeps a message for the whole session and in the dashboard's CSV export, which sits badly with "shall retain no data" in 27(1)(i). With the re-send, an official who joined 12 seconds later saw the coordinates at once. If your recording template joins the room as a participant, the same step sends it the fix; we did not test the template. - With location permission denied, the customer sees the message to allow access, and the official's console keeps showing "No GPS location yet".
- Follow the geo tag guide to host it and pass its URL as
templateUrl.
Start the recording with a close-room fallback
Call this from your server once the official has admitted the customer. If recording fails and does not recover within 30 seconds, VideoSDK closes the room, so the session cannot carry on unrecorded beyond that window. Ask the VideoSDK team whether a recovered recording is still one file, since 27(2)(ii) asks for one video file per session.
// startVcipRecording.js (your server, Node 18+)
export async function startVcipRecording({ roomId, serverToken, templateUrl }) {
  const res = await fetch("https://api.videosdk.live/v2/recordings/start", {
    method: "POST",
    headers: { Authorization: serverToken, "Content-Type": "application/json" },
    body: JSON.stringify({
      roomId,
      templateUrl, // your hosted geo-tag template, see the docs guide
      config: { mode: "video-and-audio", quality: "high" },
      // If recording fails and does not recover in 30 seconds, close the room,
      // so the session never continues without a recording.
      onFailure: { waitTime: 30, action: "close-room" },
    }),
  });
  if (!res.ok) throw new Error(`Recording did not start: ${res.status} ${await res.text()}`);
}
We ran the error path: on a room with no live session the API answered 403 "No active session found." and the function threw. We did not start a real recording in this test. Set your own bucket in the dashboard's storage configuration first, so the file lands in storage you control in India.
Build the activity log from the sessions API
Para 27(3)(ii) asks you to preserve the activity log with the credentials of the official. The sessions API returns who joined, when and why they left; store it next to the official's employee ID from your own system.
// sessionActivityLog.js (your server, Node 18+)
export async function sessionActivityLog({ roomId, serverToken }) {
  const res = await fetch(
    `https://api.videosdk.live/v2/sessions/?roomId=${encodeURIComponent(roomId)}`,
    { headers: { Authorization: serverToken } }
  );
  if (!res.ok) throw new Error(`Session fetch failed: ${res.status}`);
  const { data } = await res.json();

  // One row per join and leave, ready to store next to the official's ID.
  return data.flatMap((session) =>
    session.participants.flatMap((p) =>
      p.timelog.map((t) => ({
        sessionId: session.id,
        participantId: p.participantId,
        name: p.name,
        joinedAt: t.start,
        leftAt: t.end,
        leaveReason: t.leaveReason ?? null,
      }))
    )
  );
}
On a test room this returned one row per join and leave for the official and the customer, with times and the leave reason. Para 27(2)(ii) puts the fresh-session duty on your application: when the customer drops, end the room, create a new one for the retry, and link both sessions to the same application in your records.
For the full flow (tokens, waiting lobby, document capture, reconnect handling), follow VideoSDK's video KYC guide and our co-operative bank build guide.
Glossary
- V-CIP (Video-based Customer Identification Process) is the RBI's term for video KYC run by an authorised official of the regulated entity.
- A regulated entity (RE) is any bank, NBFC or other institution covered by an RBI KYC Direction.
- Customer due diligence (CDD) is identifying and verifying the customer and understanding the purpose of the relationship.
- An Officially Valid Document (OVD) is a document such as a passport, driving licence or proof of possession of an Aadhaar number.
- CKYCR (Central KYC Records Registry) is the registry from which a bank can download a customer's KYC records with their KYC identifier.
- A Business Correspondent (BC) is an agent a bank uses to serve customers outside branches; banks may use BCs for assisted V-CIP at the customer end.
- Concurrent audit is an audit of each V-CIP account before it is made operational.
- CERT-In (Indian Computer Emergency Response Team) is the national agency whose empanelled auditors must test the V-CIP infrastructure.
Frequently asked questions
What are the RBI guidelines for video KYC?
They are the V-CIP paragraphs of the RBI's KYC Directions, 2025: paras 26 and 27 for commercial banks and NBFCs, other numbers for other entities (see the table above). They cover where the technology runs, encryption, blocking non-India IPs, geo-tagged recordings, liveness and face match, security testing by CERT-In empanelled auditors, the call procedure, concurrent audit and storage of all data in India.
Is video KYC compulsory?
No. Each Direction says the entity "may undertake V-CIP". If a bank or NBFC has introduced V-CIP, it must offer it as the first option for remote onboarding.
Is the RBI KYC Master Direction 2016 still valid?
No. It was repealed on 28 November 2025 when the ten entity-wise KYC Directions were issued. Actions taken under it before the repeal continue to be governed by it (para 81 of the Commercial Banks Directions), but new sessions follow the 2025 Directions.
What are the new bank KYC rules for 2026?
The KYC rules in force in 2026 are the entity-wise KYC Directions, 2025. The Commercial Banks Directions were amended on 29 December 2025, 18 September 2026 and 1 October 2026, on CKYCR, foreign portfolio investors and governance. None of those amendments changes the V-CIP paragraphs.
What is mandatory during a V-CIP session?
A trained official of the regulated entity runs the call; the customer's consent is recorded; the session is recorded with live GPS coordinates and a timestamp; the official captures a photo and a clear image of the PAN card, varies the questions, and checks that the photos and details match. A dropped call needs a fresh session.
What will be asked in video KYC?
The official confirms your identity details, asks you to show your PAN card (unless you gave an e-PAN), asks questions in a varied order to confirm the call is live, and confirms your current address and financial profile. A printout of an e-document, including an e-PAN, is not accepted.
How long must V-CIP recordings be kept?
The Directions set no separate period for V-CIP. Records of customer identification must be kept for at least five years after the business relationship ends (para 50(2) for commercial banks), and the record rules apply to V-CIP.
Can the bank official do V-CIP from home?
The Directions do not set the official's location. They require the V-CIP connection to originate from the bank's own secured network domain and the official to be specially trained. Check your bank's information security policy before allowing remote officials.
Conclusion
The RBI's video KYC guidelines did not get stricter in November 2025; they moved. The rules from 2020 to 2025 now sit in ten entity-wise Directions, with new paragraph numbers and one new liveness Explanation. Start from the Direction for your entity type, map each clause to a feature and an audit artefact, and settle the encryption and recording design with your security team before you build.
Build your V-CIP flow on VideoSDK. Sign up for VideoSDK to get API keys and follow the video KYC guide. A new account comes with a $20 credit. Need Geo IP Restriction, Geo Fencing to India or the identity APIs? Talk to our team about the Enterprise plan.