


SRT (Secure Reliable Transport) is an open-source, UDP-based streaming protocol that delivers encrypted, low-latency video over unreliable networks by combining packet loss recovery with AES encryption. For developers building live contribution pipelines, implementing SRT streaming means configuring handshake modes, latency windows, and passphrase authentication correctly. This guide walks through the full implementation path, and if your end goal is viewer-facing interactive delivery, VideoSDK's interactive live streaming handles the playback side with sub-second latency over WebRTC.
Implementing SRT Streaming: A Developer's Guide
Live contribution is the hardest, least glamorous part of any streaming pipeline. Getting a camera feed from a field encoder to your media infrastructure over a hotel Wi-Fi connection or a cellular bond without dropping frames is a real engineering problem, and it is exactly the problem SRT was built to solve.
SRT, originally developed by Haivision and open-sourced in 2017 under the SRT Alliance, has become the de facto standard for reliable, low-latency contribution over the public internet. Broadcasters, cloud platforms like AWS Media Services, and open-source servers like SRS and the NGINX SRT module all support it natively. As of 2026, if you are implementing SRT streaming, you are in good company.
This guide covers the full developer path: understanding the protocol, configuring encoders, deploying an ingest server, tuning latency, and debugging the failures that will inevitably happen at 2 a.m. before an event.
What Is SRT and How It Differs From Other Protocols
SRT is defined as a transport protocol built on UDP that adds reliability, encryption, and latency control on top of the connectionless transport. Where TCP-based protocols stall waiting for retransmissions, SRT uses Automatic Repeat reQuest (ARQ) with a time-based delivery window: lost packets are retransmitted, but only if they can arrive before their playback deadline. Packets that arrive too late are dropped on purpose, because a late frame is worse than a skipped one in live video.
SRT works by wrapping your MPEG-TS payload in SRT packets, encrypting them with AES-128 or AES-256, and exchanging them over UDP with a handshake that negotiates latency, keys, and stream identity. The result is sub-second end-to-end latency over networks with real packet loss, something neither RTMP nor HLS can achieve.
The comparison with RTMP and HLS comes down to role:
| Feature | SRT | RTMP | HLS |
|---|---|---|---|
| Transport | UDP with ARQ | TCP | TCP (HTTP) |
| Typical latency | 0.5–2 seconds | 2–5 seconds | 10–30+ seconds |
| Packet loss handling | Retransmits within latency window | Head-of-line blocking | Segment retries, long buffer |
| Encryption | Built-in AES-128/256 | None in base spec | TLS via HTTPS delivery |
| Best for | Contribution over unreliable networks | Legacy ingest to CDNs | Viewer distribution at scale |
RTMP remains ubiquitous as an ingest format because every CDN and media server accepts it, but it degrades badly on lossy links. HLS is a distribution protocol, not a contribution one. SRT fills the middle: getting the feed reliably from the field to your transcoder. In practice, most modern pipelines use SRT for contribution and HLS or WebRTC for the viewer side.
Core SRT Concepts Every Developer Should Know
Every SRT implementation stands on four concepts, and misunderstanding them is the source of most connection failures.
Handshake modes. SRT connections are established in one of three modes. In caller mode, the endpoint actively dials out to a known address and port, which is what a field encoder behind NAT should do. In listener mode, the endpoint waits for incoming connections, which is what your ingest server does. Rendezvous mode has both sides dial each other simultaneously, used when both endpoints are behind restrictive NATs or when you want a symmetric connection. The most common topology mistake is pointing an encoder at a listener that is itself behind a firewall that blocks UDP.
Stream IDs. The streamid parameter is a string carried in the handshake that lets a single SRT listener port multiplex many streams. Your ingest server routes each incoming connection to the right backend application based on this identifier, similar to how an RTMP application name works.
Passphrase authentication. SRT supports AES encryption with a shared passphrase negotiated during the handshake. If the passphrases do not match, or if the key length settings differ between the two endpoints, the connection is rejected immediately. This is both an authentication mechanism and an encryption layer in one.
Packet-level parameters. The latency window, maximum payload size, and bandwidth overhead settings govern how the protocol behaves under network stress. These are set per-connection and must be compatible on both ends. We cover tuning them properly later in this guide.
Setting Up Your Development Environment
Before implementing SRT streaming, assemble a toolchain that can produce, transport, and inspect SRT streams. You need three pieces.
First, an encoder. FFmpeg compiled with libsrt support is the standard developer choice, and OBS Studio has supported SRT output since version 25. Second, an ingest server. Your options are the NGINX SRT module, SRS (Simple Realtime Server), MediaMTX, or a managed cloud ingest like AWS MediaLive. Third, inspection tools: ffprobe for verifying stream health and the srt-live-transmit utility from the SRT reference implementation for isolated transport testing.
The overall flow of an SRT contribution pipeline looks like this:
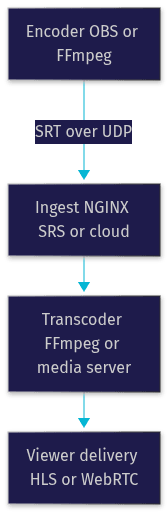
For local testing, run the ingest listener on a machine with the SRT UDP port open in its firewall, and point your encoder at it in caller mode. Verify the handshake completes before worrying about picture quality; transport problems and encoding problems are separate debugging tracks.
Configuring the Encoder for SRT
Encoder configuration is where implementing SRT streaming succeeds or fails, because every parameter here must agree with the ingest side.
The SRT URL structure. An SRT endpoint address follows a consistent pattern: the scheme, the host and port, and then query parameters carrying the streamid, passphrase, latency, and mode. The streamid tells the server which backend stream this is. The passphrase enables AES encryption. The mode parameter decides whether the encoder acts as caller or listener. When your encoder sits behind NAT or a restrictive firewall, always make it the caller dialing out to your public ingest listener, because outbound UDP generally traverses home and corporate networks without extra configuration.
Latency. This value, in milliseconds, defines the retransmission window on both ends. The two endpoints negotiate to the higher of the two configured values, so a mismatch is not fatal, but a value that is too low is. A reasonable default for public internet contribution is 120 milliseconds on a well-behaved network, rising to 500 milliseconds or more on cellular or long-distance paths.
Payload size. The maximum payload per SRT packet should stay at or below the network path's maximum transmission unit, typically around 1,312 bytes of payload to fit safely inside a standard 1,500-byte Ethernet frame. Oversized payloads cause fragmentation, and fragmented UDP packets are the first casualties of packet loss.
Encryption key length. Choose AES-128 or AES-256 by setting the pbkeylen parameter consistently on both endpoints. AES-128 is sufficient for most contribution workflows and slightly cheaper on CPU-constrained encoders like a Raspberry Pi; AES-256 is the choice when your compliance requirements demand it.
Bandwidth overhead. SRT adds retransmission and control traffic on top of your encoded bitrate. Configure an overhead of 25 to 35 percent above the media bitrate so the protocol has headroom for recovery without starving the stream.
Deploying an SRT Ingest Server
Two deployment approaches dominate production SRT ingest, and both follow the same architecture: a UDP SRT listener in front, a TCP-based media backend behind.
NGINX with the SRT module. The NGINX SRT module adds an SRT listener block to your NGINX configuration. You define the listen port, the passphrase requirement, and, critically, a mapping between incoming stream IDs and backend RTMP or MPEG-TS destinations. Each incoming SRT connection is decrypted, matched against the streamid mapping, and pushed to your media backend over TCP. This approach shines when you already run NGINX for RTMP ingest and want to add SRT as an additional front door without rearchitecting.
SRS (Simple Realtime Server). SRS supports SRT ingest natively alongside RTMP, WebRTC, and HLS output. You enable the SRT listener, set the port and mandatory passphrase, and SRS handles the demuxing into its internal pipeline, from which you can transcode and republish to HLS or WebRTC. SRS is often the faster path for developers who want one binary handling ingest through playback.
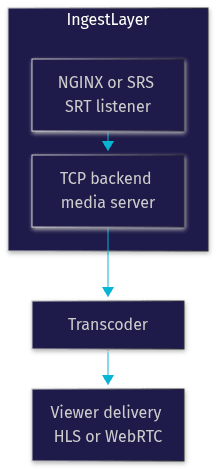
Whichever you choose, open the SRT UDP port in your cloud security group or host firewall, and remember that UDP state is different from TCP state: connection trackers and some cloud NATs handle long-lived UDP flows poorly, so enable keepalive traffic and test from a real external network, not just localhost.
Tuning SRT for Optimal Performance
SRT tuning is a small set of decisions with well-established rules of thumb, and getting them right is the difference between a rock-solid contribution link and one that stutters whenever the network hiccups.
Latency must exceed round-trip time by a healthy margin. The widely cited rule from the SRT Alliance documentation is to set the latency window to at least four times the round-trip time between endpoints. A 30 ms RTT path wants at least 120 ms of latency; a transcontinental 100 ms RTT path wants 400 ms or more. Measure RTT with a simple ping test before configuring, and remember the negotiated value is the maximum of both endpoints' settings.
Budget bandwidth for overhead. Your available bandwidth should be roughly 1.5 times your encoded bitrate. A 5 Mbps stream wants at least 7.5 Mbps of clean path capacity so retransmissions fit inside the window without compounding loss.
Keep payloads under the path MTU. Verify the maximum payload size stays below the smallest MTU on the route. If your path crosses tunnels or VPNs that shrink the effective MTU, reduce the payload size accordingly rather than letting IP fragmentation silently destroy reliability.
Match key lengths. Both endpoints must use the same encryption key length. A mismatch produces an immediate handshake rejection that looks, confusingly, like a network failure in the logs.
Enable periodic NAK and keepalive. Periodic negative acknowledgments let the receiver report loss proactively rather than waiting for the sender's own detection, which matters on high-latency paths. Keepalive packets keep NAT mappings alive on long idle stretches.
Monitoring, Debugging, and Common Pitfalls
Every SRT deployment eventually produces a connection that will not connect or a stream that connects but stutters. Debug them separately.
Tools. ffprobe attached to your SRT URL reports whether the stream is arriving and at what bitrate, which cleanly separates transport problems from encoder problems. srt-live-transmit lets you test the transport layer in isolation, pushing a test file or live source to a listener without any encoder in the loop. NGINX and SRS both log handshake results, stream ID matches, and passphrase rejections, and these logs are where the truth lives.
Connection timeout. The handshake never completing almost always means a firewall or NAT problem: the UDP port is not open on the listener side, the listener is behind a cloud security group that only allows TCP, or the encoder is configured as a listener when it should be a caller. Verify the port with a UDP test before blaming the protocol.
Mismatched passphrase. An immediate rejection after contact, with no timeout, is the signature of a passphrase or key-length mismatch. Check both endpoints, including invisible whitespace in configuration strings.
High packet loss and stutter. If the stream connects but drops frames, your latency window is too small for the path's RTT and loss profile, or your bandwidth overhead is insufficient. Raise latency first, then overhead, then re-test.
NAT traversal failures. Long-lived UDP flows get dropped by aggressive NATs. Keepalive settings and caller mode from the NAT'd side resolve most cases; rendezvous mode handles the stubborn ones.
Security Best Practices
SRT's security model is straightforward but must be applied deliberately. Always require a passphrase on public ingest listeners; an open SRT port is an open relay for anyone who discovers it. Use AES-256 where compliance requires it, and rotate passphrases between events rather than reusing one indefinitely, since the passphrase is both your authentication and your encryption key.
Restrict the ingest UDP port at the firewall to known encoder IP ranges where possible. Treat the stream ID as routing metadata, not as a secret; authentication belongs in the passphrase. For defense in depth, run your ingest listener inside a private network segment and expose it through a gateway that also enforces connection limits, so a single compromised encoder cannot flood the backend. Finally, monitor handshake rejection logs: a spike in failed passphrases on a public port is reconnaissance, not noise.
Real-World Example: Building a Low-Latency Contribution Pipeline
Consider a developer building a live event platform for a conference with a remote keynote speaker presenting from a hotel room. The requirements: sub-3-second glass-to-glass latency to the online audience, resilience over hotel Wi-Fi, and encrypted transport because the content is embargoed.
The team chose SRT for the contribution leg after testing RTMP first. Over the hotel's congested Wi-Fi, RTMP's TCP connection stalled repeatedly on packet loss, producing multi-second freezes. Switching the OBS encoder to SRT output in caller mode, pointed at an SRS ingest server in the cloud, stabilized the link immediately.
The decision points along the way illustrate the whole guide. The encoder was configured as a caller because it sat behind hotel NAT, dialing out to the public ingest listener. The stream ID identified the keynote session so the ingest could route it to the correct transcoder. A 400 ms latency window was chosen after measuring roughly 90 ms RTT to the ingest region, following the four-times-RTT rule. AES-256 with a per-event passphrase satisfied the embargo requirement. Bandwidth overhead was set to 30 percent above the 4 Mbps encoded bitrate.
On the server side, SRS decrypted the incoming stream, republished it into its internal pipeline, and delivered HLS to the bulk audience while a low-latency WebRTC path served the moderator who needed to interact with the speaker in real time. The team monitored the link with ffprobe during the event, watching for bitrate dips that signaled the hotel network degrading, and had a pre-agreed fallback of raising the latency window to 800 ms if loss spiked.
The event ran without a dropped frame. The lesson: SRT's parameters are not knobs to fear, they are decisions to make deliberately, based on measured network conditions.
For teams whose end goal is interactive viewer delivery rather than one-way broadcast, VideoSDK's interactive live streaming provides sub-second audience interaction on the playback side, complementing an SRT contribution front end. And if you control both ends of the pipeline, VideoSDK's video calling SDKs handle transport, reconnection, and adaptive bitrate natively over WebRTC without any manual latency tuning.
Definitions Glossary
SRT (Secure Reliable Transport): An open-source UDP-based transport protocol that adds encryption, packet loss recovery, and latency control for live video contribution over unreliable networks.
ARQ (Automatic Repeat reQuest): The retransmission mechanism SRT uses to recover lost packets within a time-based delivery window, dropping packets that would arrive too late for playback.
Handshake mode: The role an SRT endpoint takes when establishing a connection: caller (dials out), listener (waits for connections), or rendezvous (both dial simultaneously).
Stream ID (streamid): A string carried in the SRT handshake that lets a single listener port multiplex and route multiple incoming streams to different backend destinations.
Latency window: The time-based buffer, in milliseconds, during which retransmitted packets can still be delivered in time; the negotiated value is the higher of the two endpoints' settings.
Passphrase: The shared secret negotiated during the SRT handshake that provides both authentication and the key material for AES-128 or AES-256 encryption.
Key Takeaways
- SRT delivers encrypted, sub-second contribution over lossy public networks by combining UDP, ARQ retransmission within a latency window, and built-in AES encryption.
- Set the latency window to at least four times the measured round-trip time, and budget roughly 1.5 times your encoded bitrate in available bandwidth for recovery overhead.
- Make encoders behind NAT the caller, keep your ingest listener's UDP port open, and always require a passphrase on public ingest endpoints.
- NGINX with the SRT module and SRS are the two dominant self-hosted ingest approaches, both following a UDP listener to TCP backend architecture.
- Debug transport and encoding separately using ffprobe and srt-live-transmit, and treat immediate handshake rejection as a passphrase mismatch rather than a network failure.
Further Reading
The SRT Alliance technical documentation on GitHub is the authoritative reference for protocol parameters and the reference implementation. The SRS project covers SRT ingest configuration in depth, and the NGINX SRT module repository documents stream ID mapping. For the viewer-facing side of your pipeline, explore VideoSDK's interactive live streaming docs and join the VideoSDK Discord community to discuss real-time delivery architecture with other developers.
What are you building with SRT? Drop a comment, I'd love to hear what kind of contribution pipeline you're working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ